Agentic AI security
Your next security risk could be an AI agent doing exactly what you authorized, with more access than the task requires.
Agentic AI brings software closer to executing business operations. Agents access systems, use tools, and take actions toward a goal.
For executives, the opportunity is faster execution. The responsibility is defining how much authority you delegate.
An AI agent goes beyond generating an answer. Within defined permissions, an agent uses tools, accesses information, and takes actions toward a goal.
For your enterprise, examples include:
- Investigating a customer issue across several systems.
- Processing invoices and routing exceptions.
- Investigating security alerts and initiating an approved response.
The opportunity is faster execution.
The security challenge is controlling access and actions throughout the workflow.
An agent with excessive permissions, exposed credentials, or manipulated instructions puts business systems and sensitive data at risk.
My takeawayDefine the work and the boundaries before granting an agent access.
Start with five questions:
- Which business problem will the agent solve?
- Which systems and data does the agent need?
- Which actions require human approval?
- How will your team monitor behavior and stop execution?
- Who owns the outcome when something goes wrong?
Keep a human on the loop, with visibility and authority to intervene.
Require approval before high-impact actions.
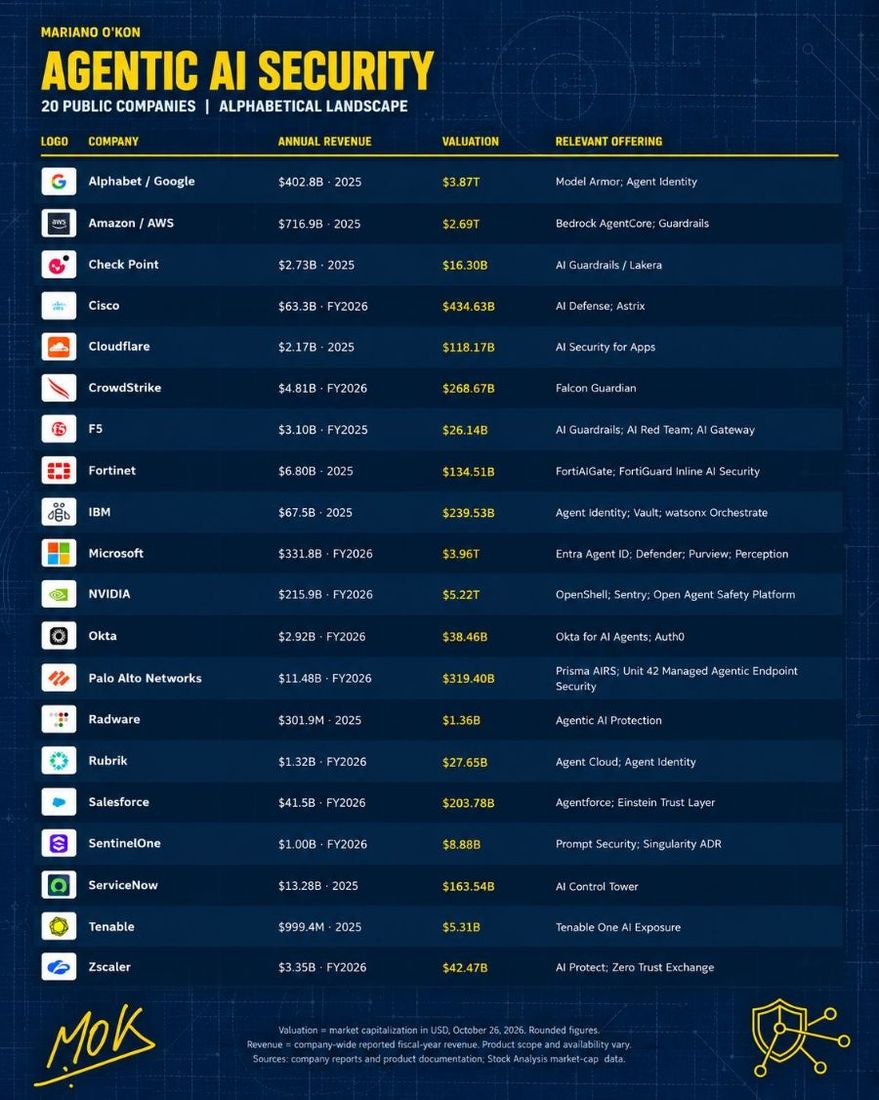
Choose security solutions around your workflows, permissions, and risks.
Which business action would you authorize an AI agent to perform today?
Mariano O'Kon speaks and advises on AI, cybersecurity, networking, infrastructure and the business impact of technology. Full bio